
This Web3/Solidity-based wargame is akin to a hacking Capture The Flag (CTF) challenge, where each level presents a smart contract puzzle waiting to be ‘hacked’. It’s an immersive and interactive way to learn about Ethereum and Solidity programming. Let's take a look at the Ethernaut Level 4 Walkthrough: Telephone
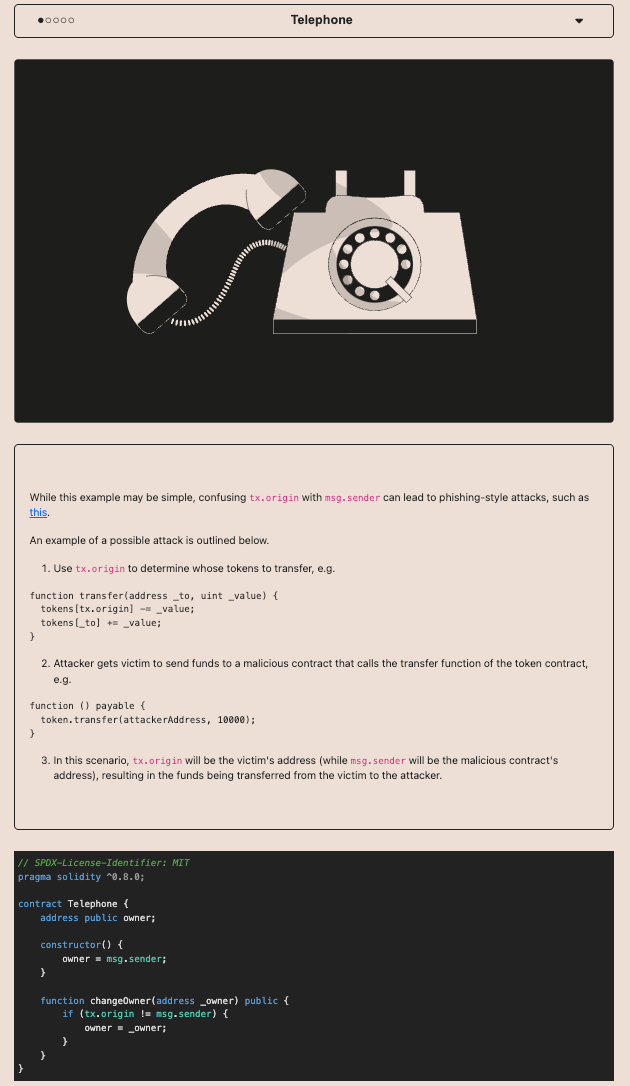
Telephone: Owning Up to the Deceptiveness of tx.origin
In the intriguing world of Ethereum smart contracts, security is paramount. Today, we’ll delve into Challenge 4: Telephone, a clever puzzle that exposes a vulnerability in how contracts identify message originators. By the end, we’ll not only conquer the challenge but gain valuable insights into the intricacies of tx.origin and msg.sender.
The Challenge’s Call
Challenge 4 presents a seemingly straightforward objective: claim ownership of a pre-deployed smart contract. But there’s a catch! Directly calling the contract’s changeOwner function won't grant ownership. This compels us to think outside the box and exploit a clever trick.
Unveiling the Contract’s Secrets
The first step is to understand the contract’s logic. We need to dissect how it verifies ownership claims. Here, the key lies in differentiating between two crucial variables:
tx.origin: This represents the original initiator of the transaction, the user's wallet address.msg.sender: This signifies the address directly calling the function, which could be another contract.
The Art of Deception
The vulnerability lies in the fact that a contract can’t directly determine tx.origin. Here's where the magic happens:
- We craft a new smart contract, let’s call it
Impersonator. Impersonatormirrors thechangeOwnerfunction from the Telephone contract.- The twist: When called,
Impersonator'schangeOwnerfunction relays the call to the Telephone contract'schangeOwner, but with a crucial twist.
The Grand Illusion
Instead of directly calling Telephone’s changeOwner, Impersonator acts as a middleman. This seemingly insignificant step alters how the Telephone contract perceives the message origin. Because Impersonator calls Telephone's changeOwner, msg.sender becomes Impersonator's address, while tx.origin remains our user wallet.
The Telephone contract, lacking the ability to see tx.origin, gets deceived. It believes Impersonator is claiming ownership, while in reality, the transaction originated from our wallet, making us the true owner.
Beyond the Challenge
Challenge 4 sheds light on the potential pitfalls of relying solely on msg.sender for authorization. It emphasizes the importance of considering tx.origin when necessary to prevent ownership manipulation or other vulnerabilities.
The Road Ahead
The Ethernaut challenges provide a fantastic platform to explore the intricacies of smart contract security. Each challenge unveils new concepts and challenges our understanding of Solidity. As we venture further, stay tuned for more explorations into the captivating realm of Ethereum smart contracts!
This blog post explores Challenge 4, highlighting the significance of understanding tx.origin and msg.sender for robust smart contract design. By exploiting the limitations of message origin identification, we not only conquered the challenge but gained valuable security insights.
Ready for the next Ethernaut challenge? Click to check out the previous ethernaut challenge and see what's next in our series!
FAQs
What is the Ethernaut Level 4: Telephone challenge?
- The challenge involves interacting with a smart contract to change ownership by exploiting specific conditions in its code.
How do you solve the Ethernaut Level 4: Telephone challenge?
- Solve it by using another contract to call the target contract’s function, thereby bypassing the direct call restriction.
What skills are needed to complete Ethernaut Level 4?
- A basic understanding of Ethereum, Solidity, and how smart contracts operate is essential.
What tools are required for the Ethernaut challenges?
- Tools like Remix IDE, Metamask, and a solid understanding of Ethereum's test networks are necessary.
What is the importance of the Telephone challenge in learning Ethereum?
- It teaches about function visibility, contract interaction, and security considerations in smart contract development.

Written by
Sven Daneel
Sven Daneel is a smart contract auditor and security educator passionate about fortifying on-chain systems. He guides engineers through foundational smart contract vulnerabilities—from pseudo-randomness exploits to authentication risks like tx.origin—helping developers spot critical security flaws before deploying to mainnet.